첫 번째 항목은 항상 핀의 출처입니다. 전체 신뢰도는 각 자료가 위의 시작·종료 시각을 얼마나 확실히 뒷받침하는지에 대한 가중 평균이며, 자료는 최신 자료보다 180일 오래될 때마다 가중치가 절반이 됩니다.
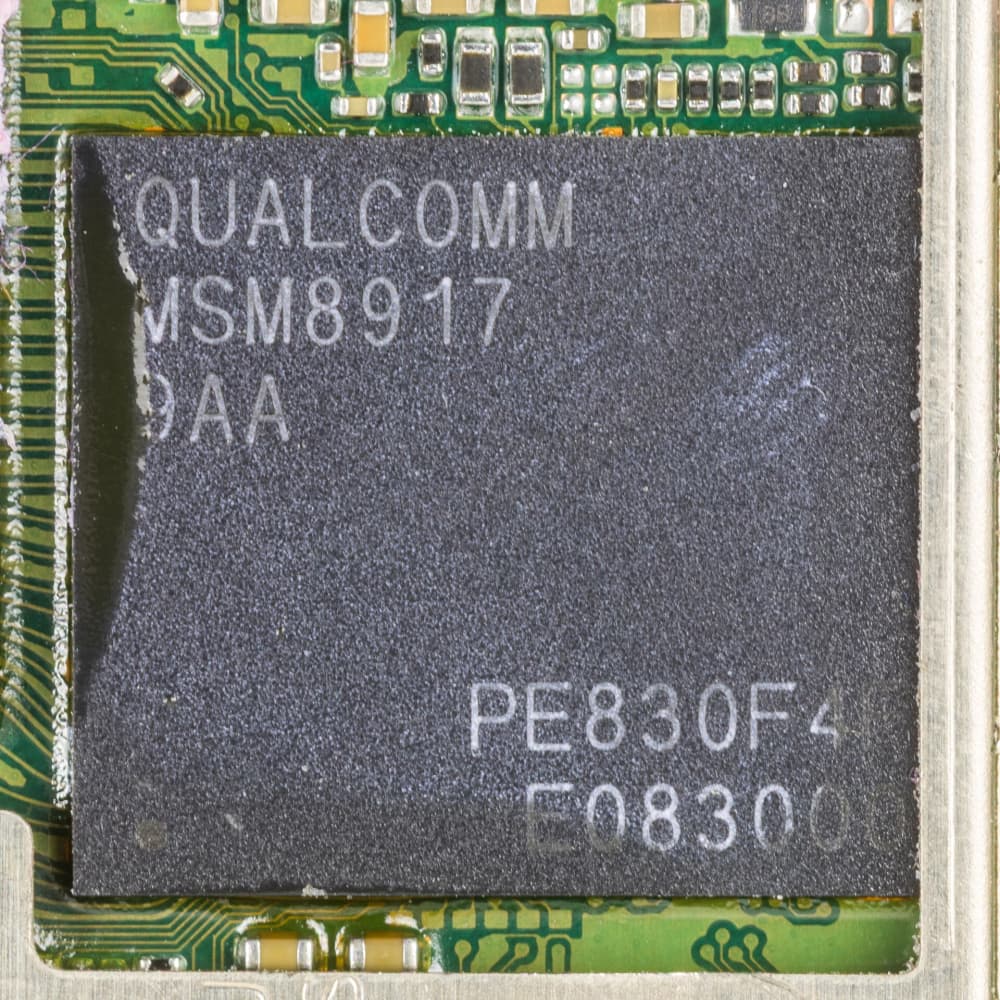
블리핑컴퓨터의 2025년 6월 2일 보도는 '월요일 공지'를 인용해 퀄컴이 'CVE-2025-21479, CVE-2025-21480, CVE-2025-27038이 구글 위협분석그룹에 따르면 제한적·표적 공격에 악용되고 있을 수 있다는 징후가 있다'고 밝혔다고 전했다.
Follow-up: Google folded the fixes for CVE-2025-21479 and CVE-2025-27038 into Android's August 2025 security update.[1]
CISA's KEV entry: 'Qualcomm[1] Multiple Chipsets Incorrect Authorization Vulnerability', added 3 June 2025, due 24 June 2025 (CVE-2025-21480 and CVE-2025-27038 were added the same day).
Quotes Qualcomm's[1] Monday advisory on exploitation and on patches reaching OEMs in May; CVE-2025-21479 and -21480 reported in late January and CVE-2025-27038 in March via the Google Android Security team.
CVSS 8.6 for the two incorrect-authorization flaws in GPU microcode and 7.5 for the Chrome-rendering use-after-free; recalls earlier Qualcomm[1] flaws used by commercial spyware vendors.
빠지거나 잘못된 점이 있나요? 이 핀을 뒷받침하는 링크, 다른 시작일이나 종료일과 그 이유, 빠지거나 잘못된 사실을 자신의 말로 알려주세요. AI가 이 핀의 출처와 대조하고 더 나은 자료를 찾아, 뒷받침하는 페이지를 추가합니다. 핀 자체의 출처가 여전히 가장 중요하게 반영됩니다. AI는 이미지도 확인합니다. 다른 것을 보여주거나 제대로 보여주지 못하는 이미지는 뒤로 옮기거나 교체합니다.
원본 제목: Qualcomm Patches Three Adreno GPU Zero-Days Exploited in Attacks